CISA orders feds to patch Zyxel flaw exploited for data theft
Attackers are now actively exploiting a high-severity vulnerability in Zyxel GS1900 series switches, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
Category
Good practices to choose, organize and use apps more safely.
1730 tips in this category.
Attackers are now actively exploiting a high-severity vulnerability in Zyxel GS1900 series switches, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
Score up to $100 off refurbished premium products, free shipping on orders of $29+, and more.
Ecommerce platform BigCommerce has alerted multiple merchants to data breaches after attackers compromised credentials for third-party Ribon applications and used them to inject malicious scripts into online stores.
Microsoft will retire the Calendar, People, and Files Microsoft 365 companion apps on December 16 and has asked admins to remove them from managed devices.
Despite admitting to a “component issue,” the company refuses to say what went wrong, how many units are affected in how many countries, and why it won’t recall its $500 AI.
Ireland's Data Protection Commission (DPC) has fined Google €403 million ($463M) for multiple GDPR violations related to processing users' location data.
Microsoft has fixed a known issue that causes copy-and-paste failures for Excel users after installing the September 2026 security updates.
The FBI's CJIS Security Policy v6.1 strengthens requirements around encryption and vulnerability scanning while continuing the shift toward more continuous security assessment.
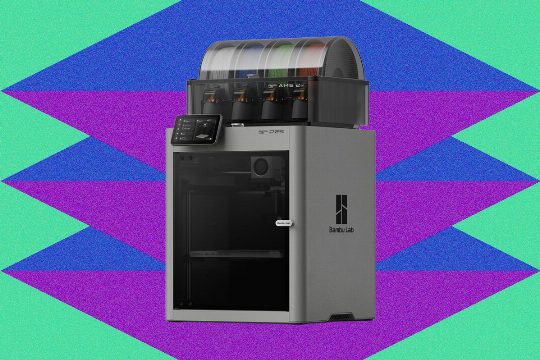
The Bambu Lab P2S Combo makes useful, polished objects without requiring advanced technical.
WIRED dedicating an entire issue to women in 2026 might seem regressive, or obvious, or even unnecessary.
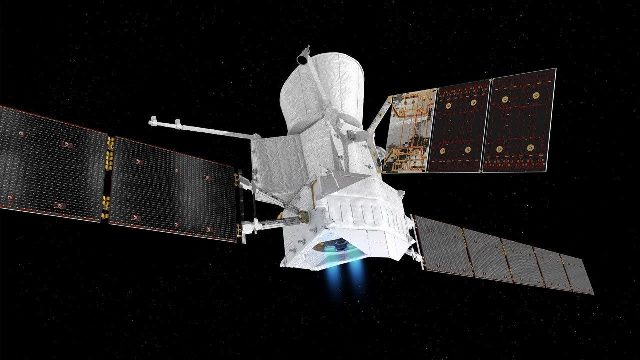
Following a difficult journey, the probe will soon begin unravelling the mysteries of Mercury’s magnetic field and internal.
An ongoing npm malware campaign involving the 'indexed-btree' package shows how threat actors bypass supply chain defenses by hiding malicious code in a package's normal runtime behavior rather than in installation scripts.